Multi-factor authentication (MFA) asks for additional proof at sign-in. For a small business, start with accounts that control email, finances and administration. A leaked password gives someone less access when these accounts require a separate form of verification.
Identify high-impact accounts
List your services, their owners and the authentication methods available. Include email, remote access, financial portals and cloud consoles. Review admin accounts separately from the accounts staff use every day. Where several people share a sign-in, check whether individual accounts would let you track access and remove one person without affecting the others.
Pick a method and run a pilot
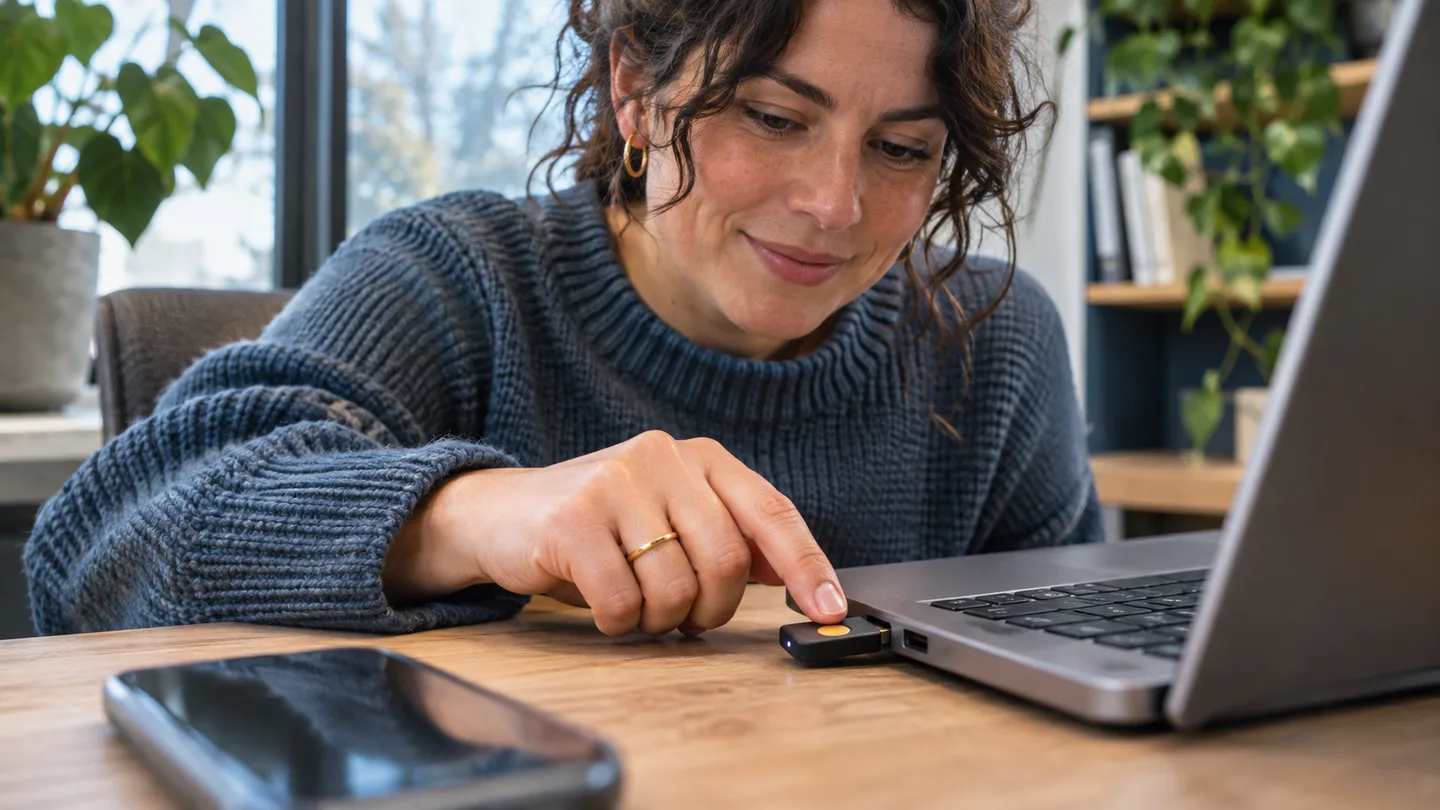
Use phishing-resistant options such as security keys or passkeys where your applications support them. Include staff who work on-site and remotely. Check that the process works on shared devices and that each participant can get back to work after replacing a phone.
Set up account recovery before a wider rollout
Document how support verifies someone’s identity before resetting an authentication method. Decide who handles after-hours requests and test recovery with the pilot group. Give staff a simple instruction for unexpected prompts. Decline the request and report it to support. Then measure coverage by counting accounts that are actually protected and recording any exceptions.
Related article Microsoft 365 employee offboarding checklist for small businesses